
The Platform
The Shift-Left API platform, step by step
From requirements to release in one platform. Generate tests from your specs and documents, with or without AI (a self-hosted model on Trial and Enterprise), run them anywhere, get failed runs explained as causes, and load and security test with the tests you already have.
RequirementsGenerateRunExplainLoad testSecureGovern
Or get the free Citizen Developer Edition →No credit card. No end date.
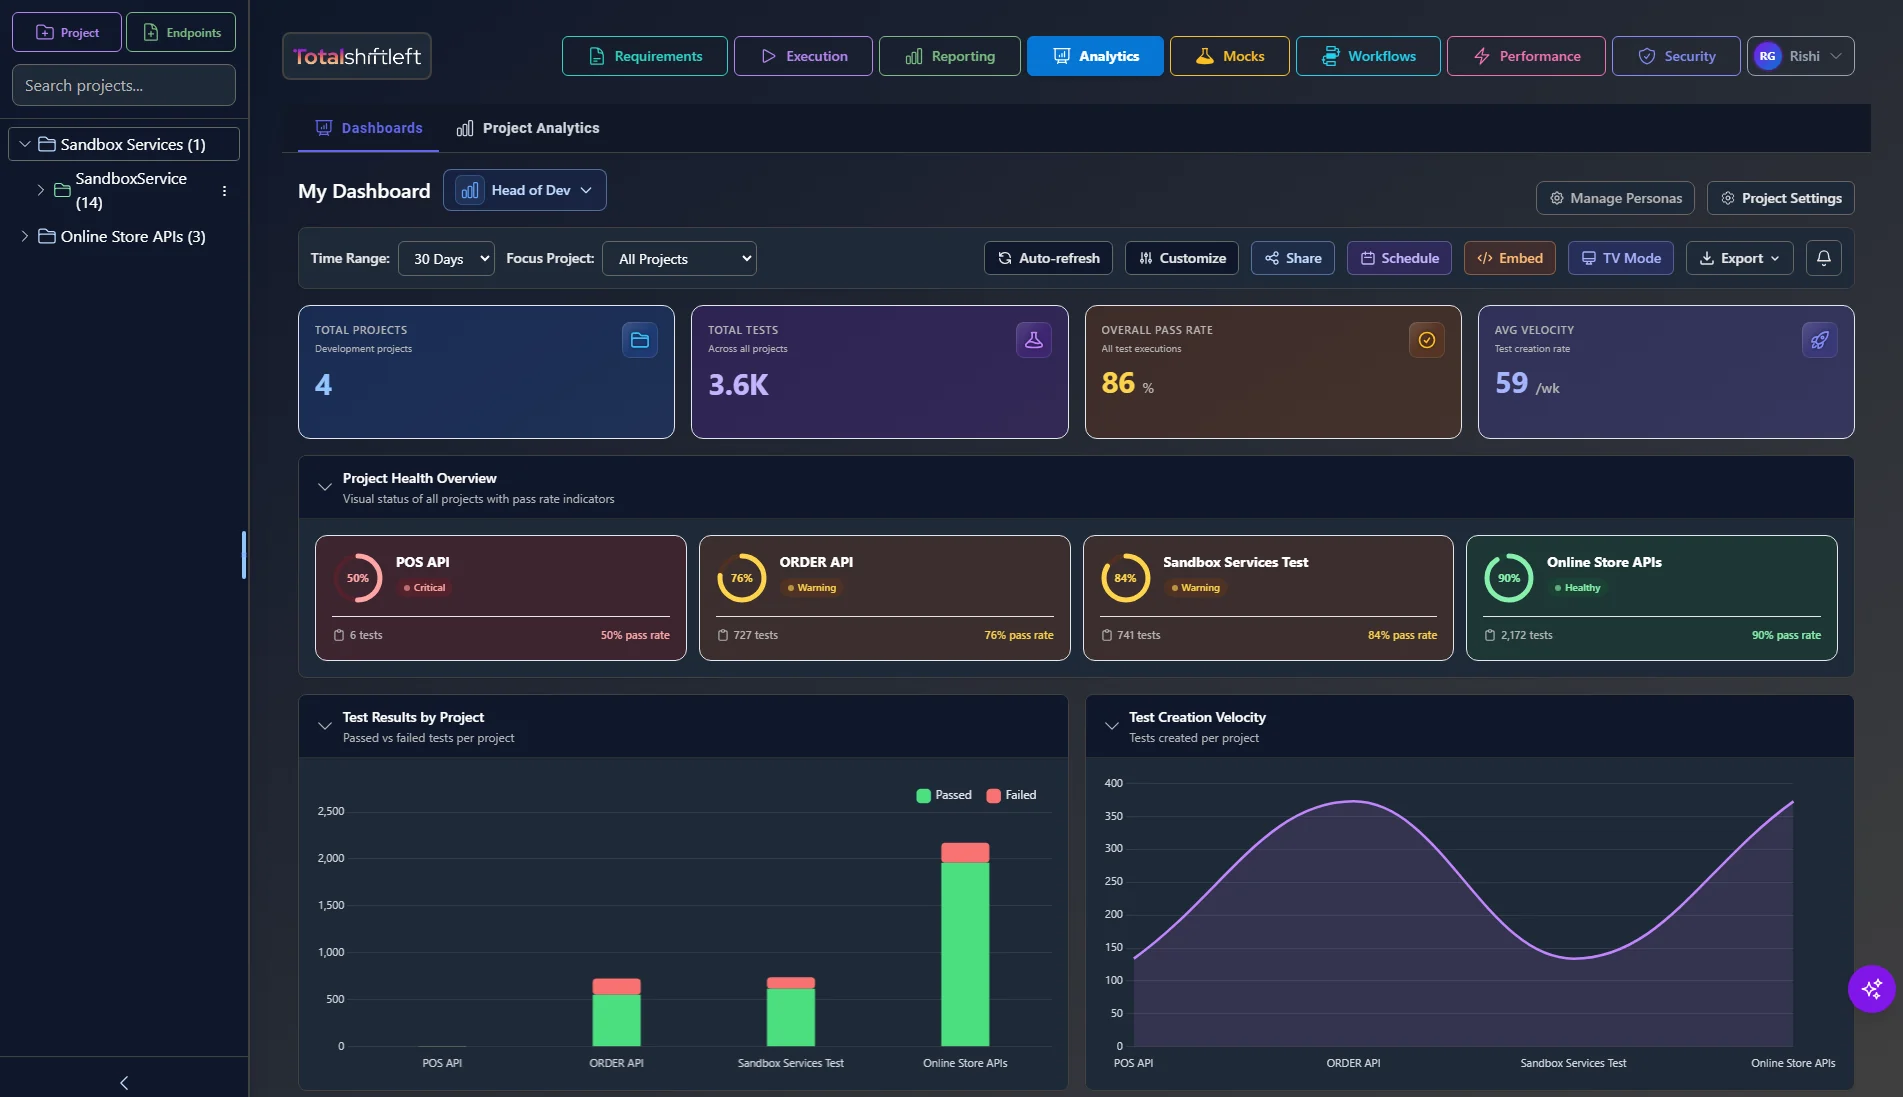
One suite, from requirement to release gate
What a single project gives you, each part explained below. Rated 4.8/5 on G2 from three verified reviews.
Guided steps
From the first requirement to the release gate
Self-hosted LLM runtimes
Ollama, LM Studio or vLLM, or a cloud provider
Assertion types
Status, fields by path, timing, SOAP, GraphQL, MCP and more
Test types, one suite
Functional, plus load and security add-ons
Platform capabilities
What's on the platform
Jump to any area: requirements, protocols, authentication, test generation, test data, runs, failure analysis, load and security testing, the assistant, mocks, analytics and governance.
Twelve steps, five phases, one platform
This is the journey you see when you sign in to Shift-Left API: from the requirement to the release gate, the load test and the security check. Each step links to the pages that explain it.
- Plan
- Build
- Run
- Understand
- Go further
Plan
Illustration Add requirements
Upload BRDs, policies, specs and Excel workbooks together. Shift-Left API extracts one requirement set, counts each rule once and holds conflicts for a person to decide.
Illustration Add your Swagger / API spec
Import OpenAPI 3.x, Swagger 2.0, WSDL, GraphQL schemas, a Postman collection or a pasted cURL into a project. Endpoints, schemas and auth come with them.
Build
Illustration Create tests
AI generates happy-path, edge-case, negative and auth tests from the spec and requirements, or you author one yourself. No code, and a coverage verdict shows the gaps to fill with one click.
Illustration Manage tests
Edit assertions, bind test data from reusable datasets, tag and organise your test portfolio, and let AI repair a test when the API changes.
Run
Illustration Execute tests
Run a test, an endpoint or a whole pack against any environment: on the server, from GitHub Actions, Jenkins or Azure DevOps (the REST API covers other CI), or on the desktop Agent for private APIs.
Illustration Schedule runs
Put test run packs on a schedule, chain them with dependencies, and let regressions surface on their own.
Understand
Illustration Read the reports
See what failed and why, grouped by cause, each with a verdict (test, data, environment or suspected defect) and a fix you can apply.
Illustration Track analytics
Dashboards for trends, reliability and coverage, by role, with scheduled reports and regression analysis across runs.
Go further
Illustration Mock APIs
Stand in for services that are not ready or not reachable yet, with static or dynamic mocks generated from the spec.
Illustration Build workflows
Chain calls into end-to-end journeys that pass data between steps, including workflows generated from your requirements.
Illustration Test performance
Load, stress, spike, soak, breakpoint, concurrency and rate-limit probe runs built from the tests you already have, with a verdict in words and targets in the traceability matrix.
Paid add-on · included in the trial
Illustration Test security
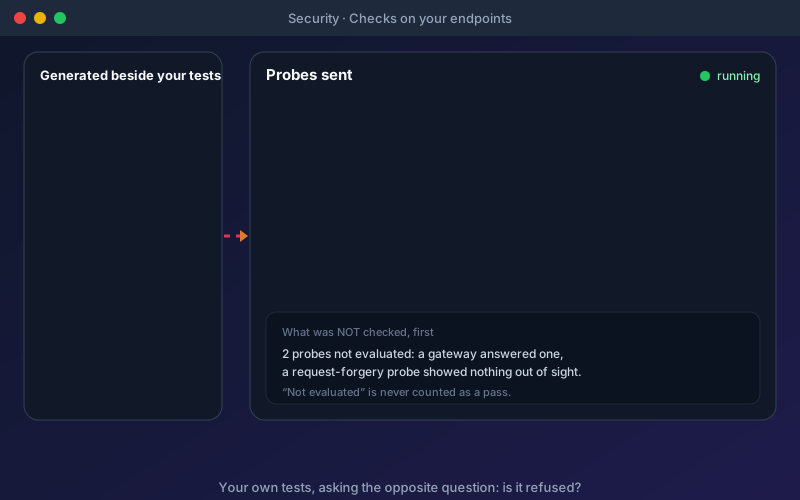
OWASP-mapped checks for authorization, injection and exposure weaknesses, including BOLA with a second test user. Every report lists what was not checked first.
Paid add-on · included in the trial
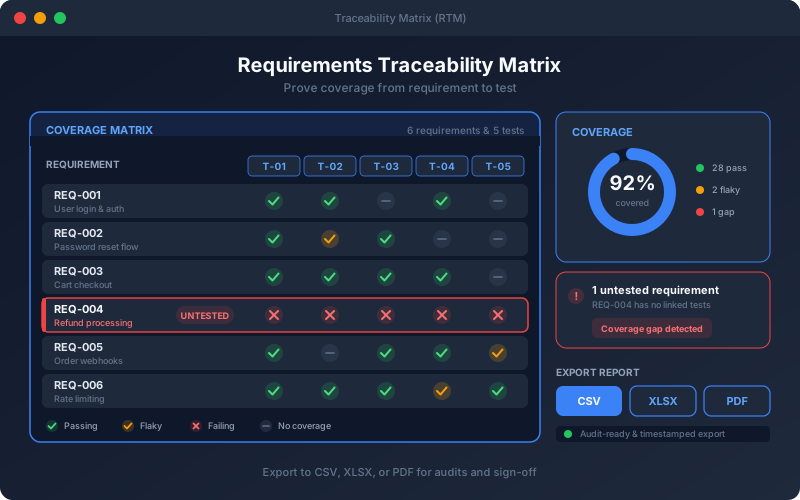
Requirements in, traceability out
Upload the documents your team already writes. Shift-Left API turns them into one requirement set and proves each requirement is tested.
In practice: upload BRDs, policies, specs and Excel workbooks together; approve the requirements; generate tests and workflows from them; read the traceability matrix.
- Many documents, one requirement set: a rule is counted once, and documents that disagree wait for a person.
- Excel read sheet by sheet: requirement rows become requirements; test data and glossaries do not.
- Traceability matrix: each requirement shows its tests, whether it was actually verified, and an Under load column.
- Workflows from requirements: end-to-end flows are found and built from your requirements and specs.
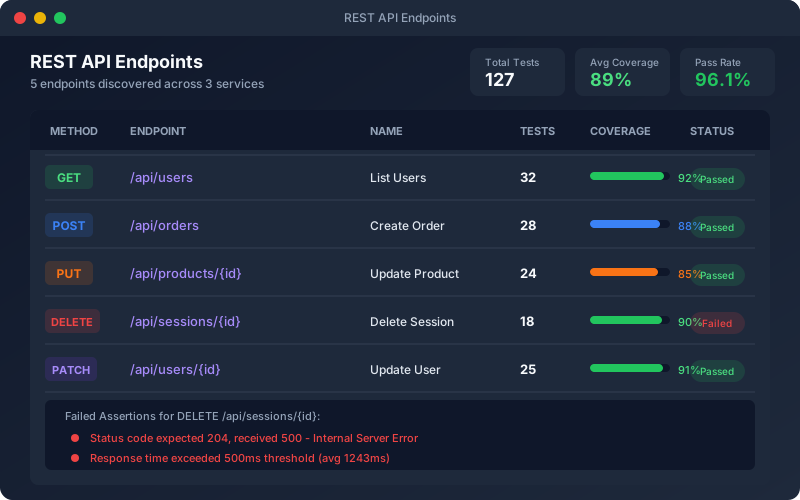
Every API style, tested in one project
Import the definitions you already have. REST, SOAP and GraphQL on every plan, with JSON-RPC, MCP servers and WebSocket-RPC on Trial and Enterprise for the newer estate.
In practice: pick the style when you import. Endpoints, assertions, mocks, workflows, packs and reports then behave the same way for all of them.
- Import OpenAPI 3.x, Swagger 2.0, WSDL, GraphQL schemas or a Postman collection (with its auth, variables and checks) from a file or a URL. Projects, features and endpoints are created for you.
- REST, SOAP with WSDL parsing and XML response assertions, and GraphQL queries and mutations with schema-driven generation and assertions on errors and data, on every plan.
- JSON-RPC 2.0 and MCP server testing (OpenRPC import, an MCP server's tools discovered as testable endpoints) and WebSocket-RPC with one authenticated connection across ordered steps, on Trial and Enterprise.
- Streaming responses: Server-Sent Events (
text/event-stream) are read into numbered events you can assert on, on every plan. How it works. - 100+ assertion types: status, headers, fields by path, types, regex, response time, SOAP, GraphQL, MCP and SSE checks, checks on the request you sent, and custom JavaScript.
- File uploads and form bodies (multipart, url-encoded, whole-file) sent the same way on every run, pack, schedule and Agent.
- Redirects and certificates set per environment, including a private CA, with certificate checking always on for production.
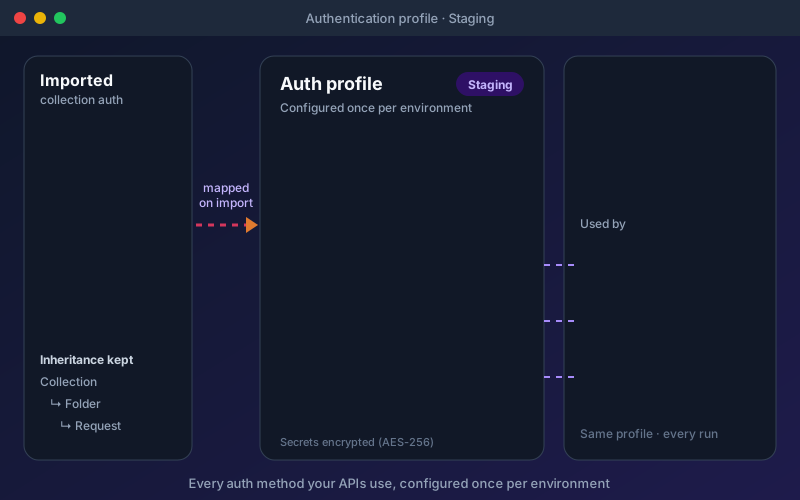
Authentication built in, configured once
Tell the platform how your API signs in per environment. Tests, workflows, mocks, load tests and security checks all reuse it.
In practice: create an auth profile, attach it to an environment, and every request that environment sends is signed the right way. Imported Postman collections map their auth into profiles.
- Every common method: API key, Basic, Bearer, Digest, NTLM, AWS Signature v4, mTLS, OAuth 1.0a, Hawk and JWT Bearer, on every plan.
- OAuth 2.0, five grant types: authorization code with PKCE, device code, client credentials, password and implicit, with the callback URL you already registered, and tokens that refresh on their own.
- Sign in with steps for logins that need a one-time code, a token exchange or a custom refresh request.
- Encrypted at rest (AES-256), and on Enterprise pulled at run time from HashiCorp Vault.
AI-powered test generation and coverage
Close coverage gaps with one-click generation; every gap your project settings allow is filled.
The platform reads your schemas and plans happy-path, edge-case and missing-parameter tests; AI (optional) polishes them.
- Generate initial tests for any endpoint to get coverage started.
- Overall coverage = status codes, parameters, request body.
- Production-grade coverage = schema, headers, auth, routing, performance, data integrity, error body.
- See a clear coverage verdict and use Generate tests for gaps to close every gap your settings allow.
- Edge cases such as boundary values and malformed input are suggested for each endpoint, and test strategy fan-out applies positive, negative, boundary, equivalence, decision-table and pairwise techniques you choose.
- AI test fix proposes a grounded repair with a before/after diff when a test fails, and API change detection classifies breaking and non-breaking changes, with before and after values for every changed field.

AI on your terms: any model, learning from your team
Choose the model, keep it inside your network if you need to, and let the generator learn from what your reviewers correct.
In practice: pick a provider under AI Settings, add your own key or point to a self-hosted endpoint, and every AI feature uses it. Switch later without losing tests or history.
- Multi-provider AI: OpenAI, Anthropic Claude, Google Gemini, Azure OpenAI or any OpenAI-compatible endpoint, with your own keys for cost control.
- Self-hosted models on Ollama, LM Studio or vLLM, so specifications and prompts stay inside your perimeter. Self-hosted API testing.
- Continuous learning: reviewer edits, deleted tests and run failures change what the generator produces next, and a Learning tab shows acceptance rate and time to green.
- You stay in control: AI proposals are reviewed and accepted by a person, and the same fixed rules, not AI, group failures and flag weak passing tests.

Test data kept apart from test logic
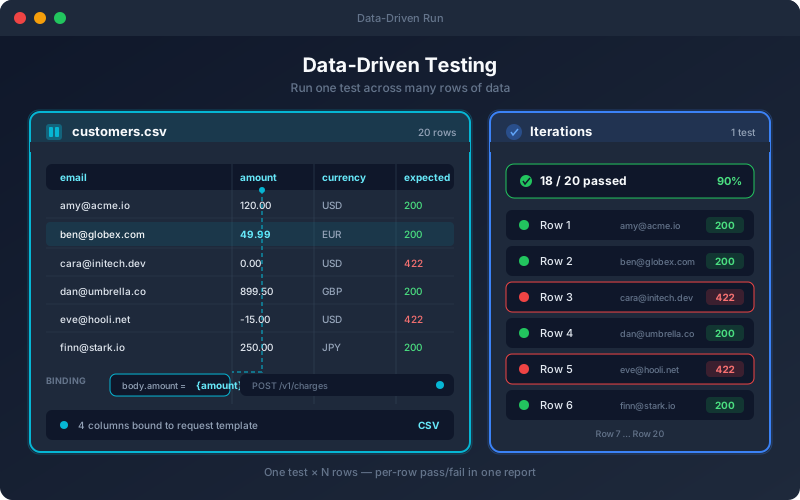
Run one test across many rows, share data across projects, and fill tests you already have without editing them one by one.
In practice: connect a data set once, bind it to a test, and read per-row results in a single report.
- Data-driven testing: a test or workflow runs once per row, with parameterized fields, headers and expected values and a per-row result.
- Reusable data sources: update a data set once and every test that uses it follows.
- Fill existing tests from a data set (CSV, Excel, JSON, YAML or XML): deliberate values and credentials are kept, with a preview first and an undo afterwards.
Run tests your way
Execute API tests on the server for CI/CD and scheduled runs, or run them locally for development and private APIs.
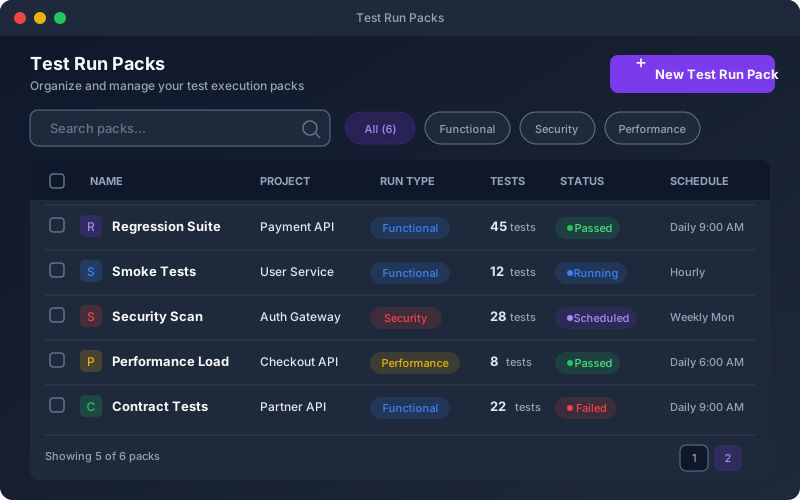
Choose the Shift-Left Engine for packs, schedules and pipelines, or the Shift-Left Agent to run tests from the Tests table on your own machine against private APIs.
- Shift-Left Engine: run packs and workflows from the GitHub Action, the Jenkins plugin or the Azure DevOps task, or trigger them over the REST API from GitLab CI, CircleCI and others.
- Scheduler: run any pack on a schedule and email the team when something fails.
- Shift-Left Agent—runs the tests in your Tests table on your own machine, for fast feedback and private endpoints. It still connects to the platform for its session token, auth profiles and result upload.
- Test run packs group tests by feature, endpoint or any criteria, with parallelism, ordering and pass-rate trends, and run against any environment.
- Signed webhooks (Professional and Enterprise) push analysed run failures, load-run results, SLO breaches and security findings to chat and incident tools, and scoped API keys drive the public REST API from scripts and pipelines.
Two ways to run
Shift-Left Engine
Best for CI/CD and scheduled runs. Always available.
Shift-Left Agent
Best for development and private APIs. Start when you need it.
Failed runs explained as causes
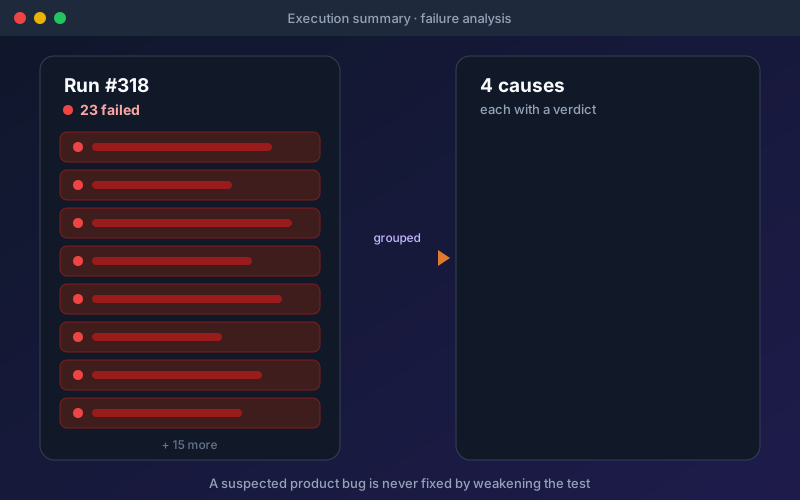
Stop scrolling red rows. A failed run is grouped into a few causes, each with a verdict and a way to fix it.
Shift-Left API reads what the server actually said, not just the status code, and asks about each cause once rather than once per test.
- A verdict per cause: test problem, data problem, environment problem or suspected product defect.
- Passing tests checked too: a green test that would not notice a regression is flagged.
- Fix that refuses to cheat: it reads the spec, the requirement and the run, and never loosens a test to make it pass.
- Regression analysis and change detection show what moved between runs and between spec versions.
Performance and load testing from your existing tests
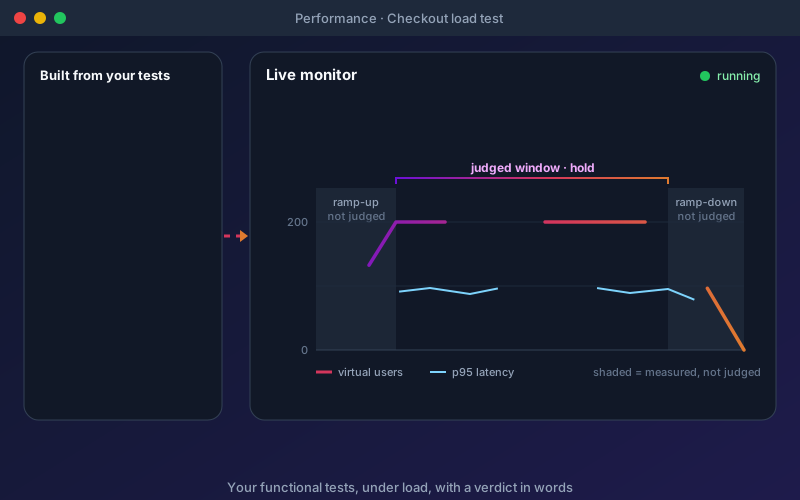
Turn functional REST, SOAP, GraphQL and JSON-RPC tests into load, stress, spike, soak, breakpoint and rate-limit tests, with no scripts.
Pick tests, choose how much traffic, set your targets and run. The report leads with a verdict in words, then the figures behind it.
- Same auth, environments and data as your functional tests, so there is nothing to rebuild.
- Performance targets such as "p95 under 800 ms" show as met or missed in the traceability matrix.
- Why a run failed: every cause in the server's own words, with the load when it began.
- Distributed load agents that connect out from your network (Team and Scale packages). How they work.
Paid add-on · included in the 15-day Trial
Starter, Team and Scale packages, from 100 to 2,000 virtual users per load generator. See the packages.
API security testing from your existing tests
OWASP-mapped checks generated beside your functional tests, aimed at the same endpoints with the same environments and credentials.
In practice: generate the checks for a project, add a second test user, run them against a test environment and read the findings. Every report starts with what it could not check, so a clean result is never overstated.
- Authorization checks: BOLA and tenant isolation with a second test user, privilege checks and mass assignment.
- Injection, SSRF and configuration: injection markers, server-side request forgery, and configuration, TLS and CORS checks.
- Findings you can act on: one finding per endpoint, check and field, with a CVSS v3.1 base score, the evidence and how to fix it. Checks are refused on production unless an administrator allows them.
- In your packs and your gate: security checks join packs, schedules and the CI quality gate, and the first-party CI steps write JUnit.
Paid add-on · included in the 15-day Trial
Added to a Professional, Custom or Enterprise licence. It detects weaknesses with benign probes and is not a penetration test. See plans and add-ons.
A Project Assistant, and an MCP server for your AI agents
Ask about your project in plain words. Connect Claude, Cursor or another MCP client to drive Shift-Left API.
Answers cite your own requirements, specs, tests and runs. Changes are proposed as cards and happen only when you accept them.
- Cited answers that open the item in the project tree.
- Approve-before-apply: run, generate, fix tests, shape packs and set up auth. It uses your own AI key, never deletes, never handles passwords, keys or tokens, and never publishes.
- Learns from corrections, per project, and you can review what it learned.
- MCP server on Professional, Trial and Enterprise. How it connects.
API mocks for development and testing
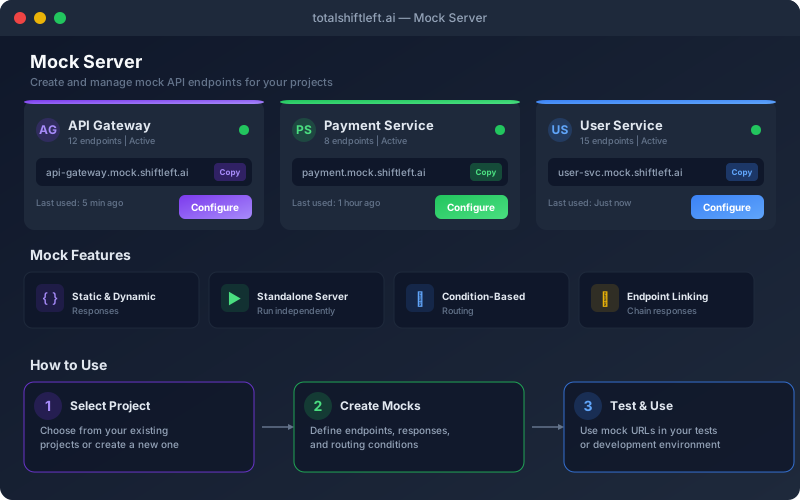
Create static or dynamic mock responses so frontend and backend teams can work in parallel without live backends.
Run mocks as a standalone server, and point an environment's base URL at the mock host when a test should hit it. Responses can depend on conditions.
- Static and dynamic responses—fixed JSON or templates with variables.
- Run mocks as a standalone server for external testing.
- Condition-based responses and endpoint linking.
Analytics and reporting
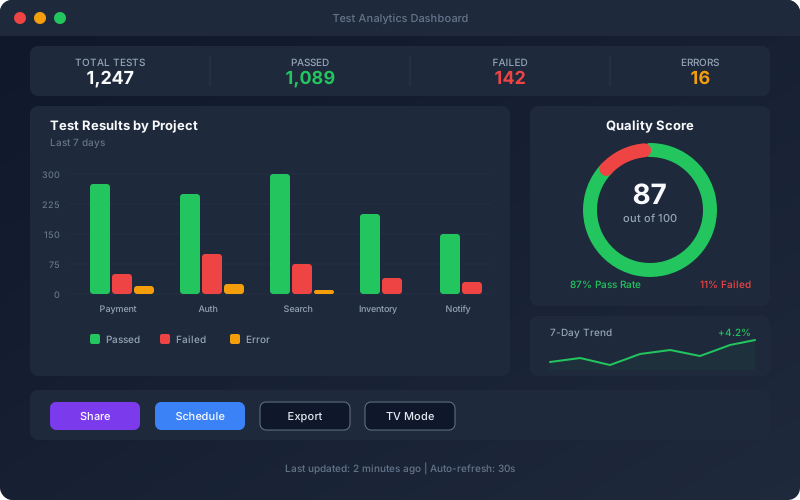
Track total tests, success rate, response time, and coverage so you can ship with confidence.
See average response time, 95th percentile, throughput, and test case creation over time.
- Total tests, success rate, failed tests, and coverage %.
- Average response time, 95th percentile, and throughput.
- Test case creation over time and most active users.
- Persona dashboards for leadership, QA, DevOps and release roles, with a full-screen TV mode, on Trial and Enterprise.
- Shareable dashboards with a secure link, password and expiry, so stakeholders see live results without an account, and scheduled reports delivered by email, both from persona dashboards on Trial and Enterprise.
- Regression analysis across runs, and a live analytics dashboard, on Trial, Professional and Enterprise.
Platform in action
Teams, governance and compliance
Control who can see and do what, prove who did it, and configure SSO with the identity provider your organization already runs.
In practice: invite people by email, give them roles per project, configure SSO with your identity provider on Enterprise or the Trial, and read the audit log when someone asks.
- Role-based access control checked by the server on every gated route, with email invitations and project assignment. Per-project roles are on Professional and above.
- Single sign-on configuration with SAML 2.0, OpenID Connect and a Microsoft Entra ID preset, and group-to-role mapping, on Enterprise and in the Trial.
- Audit logs with before and after values, IP and device, plus an activity feed and configurable retention on Enterprise and in the Trial.
- Per-project roles and team groups, with groups on Enterprise and in the Trial, and comments on tests, endpoints and projects.
- HIPAA and GDPR controls and multi-tenant isolation for regulated and multi-team deployments. Compliance overview.

Who the platform is built for
We built this for teams that need automated API quality at scale — not another API exploration tool.
Built for you if you...
- + Ship REST or SOAP APIs and need automated test coverage without writing test code
- + Lead QA and need to automate regression suites from API specifications
- + Run DevOps/Platform and want API quality gates in your CI/CD pipeline
- + Manage engineering and need visibility into API test coverage across services
- + Want to import OpenAPI, Swagger or WSDL specs and get a working test suite from them
- + Work in a regulated environment and need AI test generation that keeps specs inside your perimeter
Probably not the right fit if you...
- - Need an API documentation or design tool rather than a testing platform
- - Need gRPC, JMS, IBM MQ or Kafka testing today, where established platforms are broader
- - Have a mature custom test framework you want to keep maintaining
Every platform feature
All capabilities of Shift-Left API, organized by category, with the plan each one is on and a link to its feature page.
| Feature | Description | Plan | Details |
|---|---|---|---|
AI-Powered TestingFor Developers & QA Leads | |||
AI Test Generation | Generate a structured test suite from OpenAPI, Swagger, WSDL, GraphQL or Postman with one click, with or without an AI key. | All plans | Details |
Coverage Gaps | See exactly which tests are missing for each endpoint, and close the gaps in one click. | All plans | Details |
Edge Cases | Discover boundary conditions and edge cases humans miss. | All plans | Details |
Multi-AI | Choose OpenAI, Anthropic Claude, Google Gemini, Azure OpenAI and 15 more, or your own self-hosted model on Trial and Enterprise. | All plans | Details |
Continuous Learning | Every passing run, every edit and every requirement document teaches the platform how your API really behaves. | All plans | Details |
AI Test Fix | Repair failing tests with one click, without hiding a real API bug. | All plans | Details |
Project Assistant | Ask about your project in plain language, and let it do the work once you approve. | All plans | Details |
Requirements IntelligenceFor Business Analysts & QA Leads | |||
Requirements | Turn specs and business documents into testable requirements. | All plans | Details |
Traceability (RTM) | Prove coverage from every requirement to the tests that verify it. | All plans | Details |
Test Strategy | Generate a full test strategy across proven design techniques. | All plans | Details |
Use-Case Workflows | Approved use cases become end-to-end workflows as soon as each step has a test. | All plans | Details |
Multi-Document Requirements | Upload every BRD, policy, spec and workbook together. Rules are counted once, and disagreements wait for a person. | All plans | Details |
Test Execution & CI/CDFor DevOps & Developers | |||
Shift-Left Agent | Run API tests from your own machine, against APIs only your network can reach. | All plans | Details |
CI/CD | First-party GitHub Action, Jenkins plugin and Azure DevOps task, plus a REST API for any other CI/CD tool. | Professional+ | Details |
Scheduler | Run test packs automatically, from every few minutes to monthly, in your time zone. | Professional+ | Details |
Test Packs | Group and batch-execute tests for focused regression runs. | Professional+ | Details |
Workflows | Build multi-step API flows with a visual DAG editor. | All plans | Details |
Performance Testing | Turn the API tests you already have into load, stress, spike and soak tests, and get a verdict in words. | Add-on | Details |
Load Agents | Add machines to send more load, or load from several places, and still read one merged report. | Add-on | Details |
Redirects & Certificates | Test a redirect itself, and run against test servers with private certificates, without weakening production. | All plans | Details |
API Security Testing | OWASP-mapped checks generated beside your tests, with CVSS-scored findings and what was not checked listed first. | Add-on | Details |
Workflow Doctor | Finds what is wrong with a workflow, in plain words, and offers the fix that is safe to apply. | All plans | Details |
Test Data ManagementFor QA Engineers & Developers | |||
Data-Driven Testing | Run one test across many rows of data automatically. | All plans | Details |
Data Sources | Connect the data your tests need from the sources you already use. | All plans | Details |
Fill Tests From Data | Push a CSV, Excel, JSON, YAML or XML data set into every existing test of a project: preview first, undo afterwards. | All plans | Details |
Multi-Protocol SupportFor Architects & Tech Leads | |||
REST | Full support for REST APIs with OpenAPI and Swagger import. | All plans | Details |
GraphQL | Test GraphQL queries and mutations with schema-driven test generation. | All plans | Details |
SOAP | Test SOAP web services with WSDL import and XML response assertions. | All plans | Details |
Assertions | Validate every aspect of API responses with 100+ built-in assertions. | All plans | Details |
Mock Server | Create mock APIs for parallel development and testing. | All plans | Details |
Postman Import | Bring your Postman collections in and keep your tests. | All plans | Details |
JSON-RPC & MCP | Test JSON-RPC services and Model Context Protocol servers alongside your REST, SOAP, and GraphQL APIs. | Enterprise | Details |
WebSocket-RPC | Test RPC over WebSockets, with one authenticated connection across ordered steps. | Enterprise | Details |
File Uploads & Forms | Test multipart uploads, url-encoded forms and raw file bodies, sent the same way everywhere a test runs. | All plans | Details |
Streaming (SSE) | Read text/event-stream responses into numbered events and assert on them. | All plans | Details |
Enterprise & ComplianceFor CTOs & Engineering Managers | |||
RBAC | Control who can view and edit tests, per project. | Professional+ | Details |
Compliance Controls | Security and data-handling controls that support your HIPAA and GDPR programs. | All plans | Details |
Multi-Tenant | Isolated tenants per organization, each with its own database and subdomain. | Enterprise | Details |
Auth Profiles | OAuth 2.0, NTLM, JWT Bearer, Hawk, Digest, AWS SigV4 and more, configured once per environment. | All plans | Details |
SSO | Configure SAML 2.0 or OpenID Connect, with an Entra ID preset and group-to-role mapping. | Enterprise | Details |
API Keys | Scoped, rotatable keys for automation and integrations. | Professional+ | Details |
Webhooks | Push test events to your tools with signed, reliable delivery. | Pro & Enterprise | Details |
Secret Managers | Pull credentials from HashiCorp Vault at run time, so they never live in your tests. | Enterprise | Details |
Workspaces | Give each person a role per project, and whole teams access through groups. | Professional+ | Details |
Audit Logs | A filterable record of who changed what, when, with before and after values. | Professional+ | Details |
Comments | Discuss tests, endpoints and projects in context. | Professional+ | Details |
Analytics & MonitoringFor QA Leads & Product Owners | |||
Dashboard | Track test coverage, pass rates, and response times at a glance. | Professional+ | Details |
Regression | Track failure trends, flaky tests and slowing endpoints over time. | Professional+ | Details |
Change Detection | Detect breaking API changes before they reach production. | Professional+ | Details |
Shared Reports | Share live test reports with stakeholders via secure links. | Enterprise | Details |
Persona Dashboards | Role-tailored views for every stakeholder, plus TV mode. | Enterprise | Details |
Scheduled Reports | Deliver test summaries to stakeholders on a schedule. | Enterprise | Details |
Failure Analysis | A handful of causes with verdicts, instead of a long list of red rows. | All plans | Details |
Performance Targets | Say what "fast enough" means once, and see it judged on every run and in your requirements matrix. | Add-on | Details |
The 15-day Trial includes every Enterprise feature and both add-ons; outbound webhooks are the one feature it leaves out.
Runs in your pipeline, imports your API definitions
First-party GitHub Actions, Jenkins and Azure DevOps integrations, a public REST API for every other pipeline, and import from the API definitions you already have.
CI/CD pipelines
Run and failure events can also go to chat and incident tools through signed webhooks.
Request an integrationPlatform FAQs
Can I load test my APIs on the platform?
Yes. Performance testing turns the functional REST, SOAP, GraphQL and JSON-RPC tests you already have into smoke, load, stress, spike, soak, breakpoint, concurrency and rate-limit tests, with no scripts. It is a paid add-on to Professional, Custom and Enterprise licences (Starter, Team and Scale packages) and is included in the 15-day Trial.What API formats can I import?
OpenAPI 3.x and Swagger 2.0 (JSON or YAML), WSDL for SOAP, GraphQL schemas, and Postman collections, which bring their auth, variables and checks with them. JSON-RPC 2.0 APIs can be imported from OpenRPC on Trial and Enterprise, including the tools of an MCP server. Import from a URL or upload a file; the platform discovers the endpoints and organizes them into projects and features.How does AI test generation work?
The platform analyzes your OpenAPI/Swagger specs and endpoint schemas to suggest test cases. You can generate initial tests for an endpoint or use "Generate tests for gaps" to add tests that cover missing parameters, status codes, or request-body scenarios. Coverage is tracked as overall (functional) and production-grade (schema, headers, auth, routing, performance, data integrity, error body).How are failed runs explained?
After a run, failures are grouped into causes and each cause gets a verdict: your tests are out of date, your test data needs attention, the environment is in the way, the API itself looks broken, or there is not enough evidence to say. Grouping and verdicts come from fixed rules, with no AI and no changes to your tests; AI is used only where you allow it, to phrase the summary, investigate causes the rules could not explain and propose one fix for a whole cause. Passing tests are checked too, so a green test that would not notice a regression is flagged as "worth a look".How do I run tests in CI/CD?
Use the Shift-Left Engine for CI/CD and scheduled runs—it is always available. First-party integrations exist for GitHub Actions, Jenkins and Azure DevOps, each with quality gates. The platform also exposes a public REST API (Swagger-documented) to trigger test packs, check status, and retrieve results, which is how GitLab CI, CircleCI, Bitbucket Pipelines and other pipelines connect today.Can the platform security test my APIs?
Yes. API security testing generates OWASP-mapped checks beside your functional tests, using the same endpoints, environments and credentials: authentication, BOLA and tenant isolation with a second test user, mass assignment, injection markers, SSRF, and configuration, TLS and CORS checks. Findings carry a CVSS v3.1 base score, evidence and a fix, and every report lists what was not checked first. It is a paid add-on to Professional, Custom and Enterprise licences and is included in the 15-day Trial. It detects with benign probes and is not a penetration test.Which authentication methods can my tests use?
Auth profiles are configured once per environment and reused by tests, workflows, mocks, load tests and security checks: API key, Basic, Bearer, Digest, NTLM, AWS Signature v4, mTLS, OAuth 2.0 (authorization code with PKCE, device code, client credentials, password and implicit), OAuth 1.0a, Hawk and JWT Bearer. "Sign in with steps" covers logins that need a one-time code or a custom token refresh. Credentials are stored with AES-256 encryption, and Enterprise and the Trial can pull them from HashiCorp Vault at run time.How does test data work?
Reusable data sources feed data-driven tests, which run once per row and report pass or fail per row in one report. "Fill tests from data" pushes a CSV, Excel, JSON, YAML or XML data set into tests you already have, with a preview before anything is written and an undo afterwards. Test data stays separate from test logic, so updating a data set updates everything that uses it.What governance and access controls are there?
Role-based access control with per-project roles, an audit log with before and after values, comments on tests and endpoints, signed outbound webhooks, and scoped, rotatable API keys. Enterprise and the Trial add SSO configuration (SAML 2.0, OIDC and a Microsoft Entra ID preset) with group-to-role mapping, team groups, HashiCorp Vault secret references, the activity feed and configurable audit retention. Each tenant on the hosted service has its own database, and controls such as encrypted secrets and credential redaction support HIPAA and GDPR programs. Self-hosted deployment keeps data on infrastructure you control.How does the AI learn from my team, and which models can it use?
Generation can use OpenAI, Anthropic Claude, Google Gemini, Azure OpenAI or any OpenAI-compatible endpoint, including self-hosted models on Ollama, LM Studio or vLLM (Trial and Enterprise), with your own keys. The platform learns from passing runs, reviewer edits, deleted tests and run outcomes in each project and uses them to improve what generation and repair produce next; a learning panel shows acceptance rate, edit distance, time to green and flake rate. You can also fan one endpoint out across test design techniques such as boundary values, equivalence classes, decision tables and pairwise combinations.
Try a lesson before you try the product.
Run real REST, GraphQL, and SOAP requests against a live sandbox — no signup, no install. 32 free, hands-on lessons covering protocols, authentication, contract testing, and AI-assisted testing.
Related reading
Guides on API test automation, CI/CD integration and shift-left practice, and where the platform fits.
- What Is Shift Left Testing? Complete Guide
- How to Automate API Testing Without Code
- API Test Automation with CI/CD
- Shift-Left Testing Framework
- AI API Testing: The Complete Guide
Where it fits
Point it at your own API
The 15-day trial unlocks the Enterprise feature set and both add-ons, outbound webhooks excepted. A single user can stay on the free Citizen Developer Edition, which has no end date and is renewed free every 6 months. No credit card for either.