
Security & Compliance Controls
Security and data-handling controls that support your HIPAA and GDPR programs.
What It Does
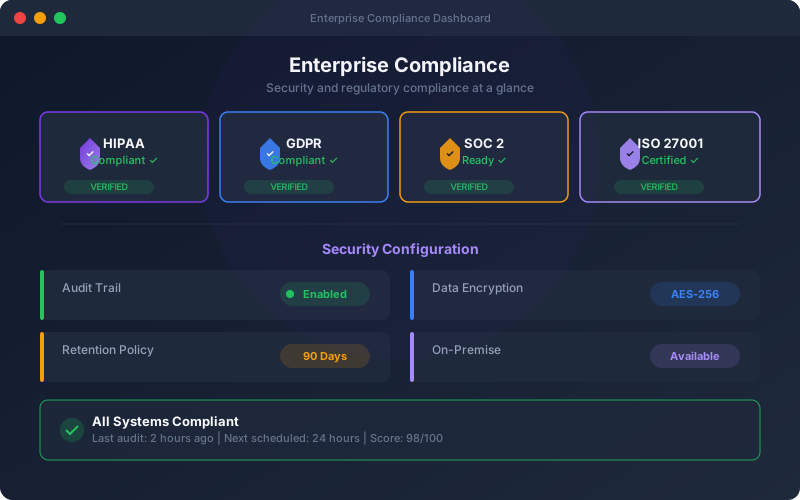
Regulated teams need to test APIs that handle health records, payments and personal data without the test platform becoming a new place for that data to leak. These controls are built into the platform rather than switched on as a module. Field-level encryption protects the secrets the platform holds: auth profiles, data-source credentials, webhook and SSO secrets, AI keys and SIEM or ticketing credentials. Each is sealed with a data key that is wrapped by a key bound to the installation, so the keystore file or the database alone is not enough to read them. Test definitions, request and response bodies and run results are not field-encrypted; their protection at rest depends on how your database is deployed, which is one reason many regulated teams self-host. Authorization headers are redacted in captured diagnostics, and audit snapshots blank any password, secret, API key or token. Role-based access control with five roles and per-project overrides limits who can see and change what, and SSO configuration with group-to-role mapping is available to Enterprise administrators. For audits, the audit trail records who changed what and when, and the security add-on rolls findings up by OWASP API category against PCI DSS 4.0, SOC 2, ISO 27001, NIST SSDF, GDPR, HIPAA, NIS2, DORA, NIST SP 800-53, EU CRA and CMMC, citing each control as evidence of testing. The add-on also checks API responses for exposed personal data and secrets.
Overview
Shift-Left API does not make you HIPAA or GDPR compliant, and no testing tool can. What it gives regulated teams is a set of controls that keep sensitive material safe while you test, and evidence your auditors can use. Secrets such as auth-profile credentials, webhook signing secrets and SSO client secrets are encrypted at rest with AES-256-GCM envelope keys. Credentials in captured request headers are redacted before they are stored or leave the local runner. Each tenant's data lives in its own database, changes are recorded in an audit trail, and you can deploy on your own infrastructure with a self-hosted model so specs, test data and prompts stay inside your network. With the security testing add-on, findings roll up against eleven frameworks, including HIPAA, GDPR, SOC 2 and ISO 27001, as evidence of testing, not certification.
Key Capabilities
How It Works
- 1
Keep credentials in auth profiles, or in HashiCorp Vault on Enterprise and Trial; they are encrypted and never copied into tests
- 2
Choose where to run: the hosted service with a database per tenant, or your own infrastructure
- 3
On Enterprise or Trial, point AI features at a self-hosted model and set how long audit records are kept
- 4
Give each person the role their work needs, per project where required
- 5
For audit evidence, use the audit log and, with the security add-on, its framework view
Available on
All Plans
Included in the free trial — no credit card required.
Documentation
Step-by-step guides for setting up and using Compliance Controls.
Built for regulated teams
Teams in regulated industries rely on this capability to ship API changes with an audit trail.
Go deeper
Guides and playbooks that show this capability in practice.
Try Compliance Controls Today
Start your 15-day free trial — no credit card required.