
Outbound Webhooks
Push test events to your tools with signed, reliable delivery.
What It Does
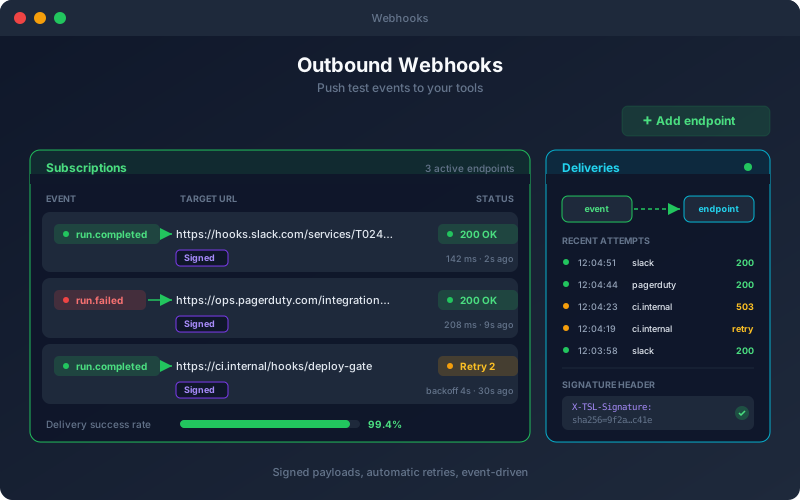
Outbound Webhooks turn the platform into an event source your other systems can react to. Register a subscription with the URL you want notified and the events you care about, and the platform posts a signed JSON payload to that endpoint whenever those events occur. When a pack run fails, the run.triaged event arrives after failure analysis has grouped the failures into causes, so the receiver gets the explanation, not just a red count. Load-run completions, SLO breaches and security findings travel on the same stream. Signature verification lets your receiver trust the call, retries ride out short outages, and anything still undelivered after five attempts stays in the delivery log for a one-click redeliver. Payloads are generic JSON, ready for your own service, an incident tool or a chat workflow.
Overview
Subscribe your systems to platform events (analysed run failures, load-run completions and SLO breaches, security scan results and findings, approvals, mentions and more) and receive them as outbound webhooks the moment they happen. Every delivery is signed with HMAC-SHA256 so your endpoint can verify it came from the platform, and a failed delivery is retried up to five times with exponential backoff. Subscribe to every event or a list, for all projects or one, and inspect the last 100 deliveries. Webhooks are available on Professional and Enterprise; they are not part of the 15-day Trial.
Key Capabilities
How It Works
- 1
Create a webhook subscription with a target URL and events
- 2
Copy the signing secret, shown once, into your receiver
- 3
The platform signs and posts payloads when those events fire
- 4
Your endpoint verifies the X-SLS-Signature header and processes the event
- 5
Review delivery history, redeliver or rotate the secret in settings
Available on
professional Plan & Above
Upgrade to the professional plan to unlock this feature.
Documentation
Step-by-step guides for setting up and using Webhooks.
Go deeper
Guides and playbooks that show this capability in practice.
Try Webhooks Today
Start your 15-day free trial — no credit card required.