SOAP API Testing: How to Test WSDL Web Services
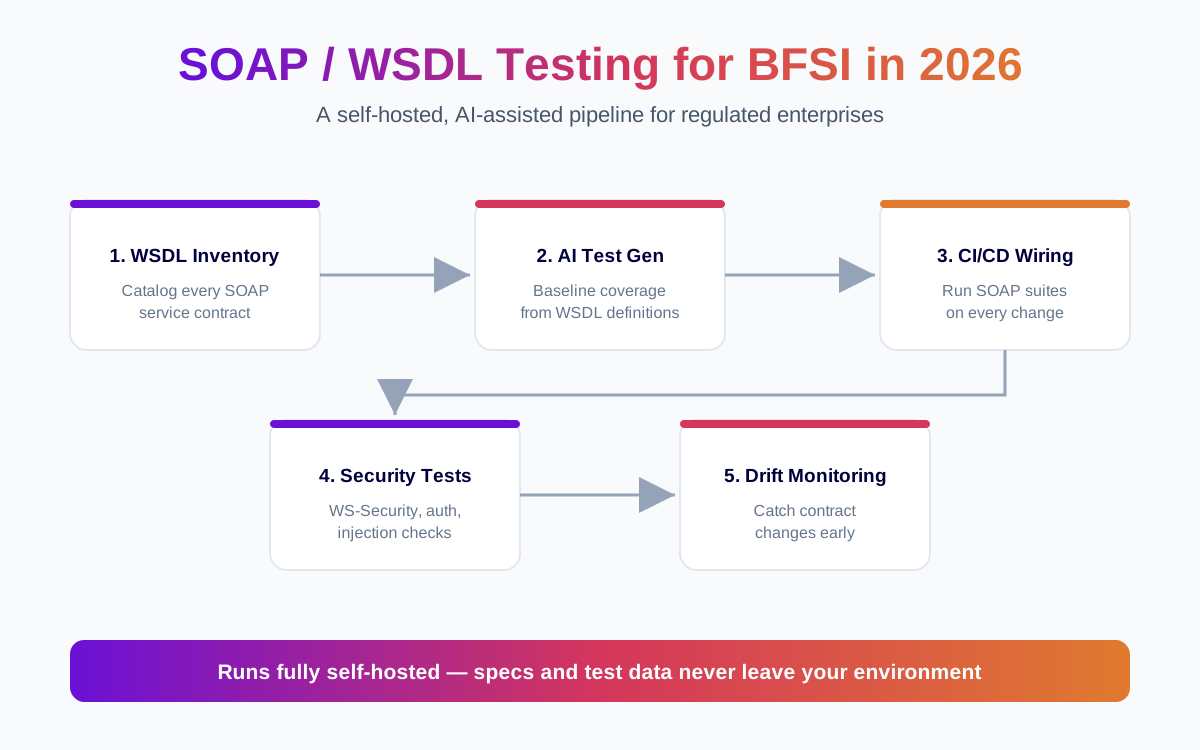
How to test SOAP APIs: envelopes, WSDL, faults and namespaced XPath, SOAP vs REST testing, the test cases to cover, tools, CI/CD, and what changes in banking and other regulated industries.
7 articles
How to test SOAP APIs: envelopes, WSDL, faults and namespaced XPath, SOAP vs REST testing, the test cases to cover, tools, CI/CD, and what changes in banking and other regulated industries.
How GDPR, Schrems II, and equivalent data-residency rules apply to API testing — captured payloads, AI inference paths, and run-report storage. EU SCC, transfer impact assessments, and the patterns that survive a DPA review.
How to run modern API testing — including AI-assisted test generation — inside fully air-gapped environments. Patterns for classified, DoD IL5/IL6, sovereign-cloud, and regulated-industry deployments where no outbound network is permitted.
How API testing programs evidence NIST SP 800-53 Rev. 5 controls for FedRAMP Moderate / High and StateRAMP authorizations. Boundary discipline, AI policy alignment, and change-management evidence designed for the SSP.
Which SOC 2 Trust Service Criteria are evidenced by API testing, what the artifacts look like, and how to design a program that reduces auditor back- and-forth. Worked control mappings for CC7, CC8, and Availability.
How API testing programs satisfy PCI-DSS v4.0.1 controls without expanding cardholder-data scope. Tokenization-aware test fixtures, in-scope vs out-of- scope tooling, and a control-mapping cheat sheet for payment teams.
How to design API testing programs that satisfy HIPAA Security Rule controls without leaking PHI to third-party AI services. PHI masking, BAA-friendly tooling, audit evidence, and a control-mapping cheat sheet.